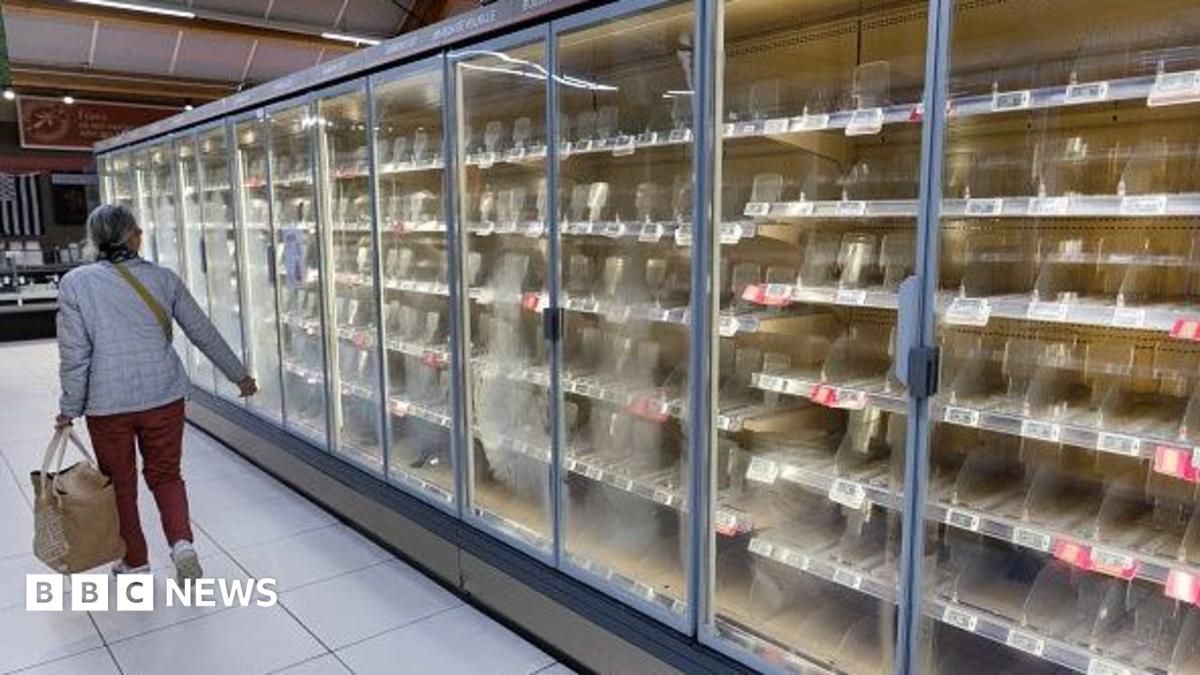
Supermarkets across Europe have recently experienced a cyber-attack that impacted their refrigeration systems, highlighting the potential vulnerabilities of internet-connected devices. This incident raises important questions about the safety of everything from industrial equipment to everyday home appliances.
Smart devices like refrigerators, heating systems, and washing machines, while convenient, can also be susceptible to hacking if not properly secured. Although major manufacturers typically implement strong security measures, vulnerabilities have been identified in the past. For instance, a 2015 study revealed how a flaw in a Samsung smart fridge allowed unauthorized access to internet traffic.
The Importance of Cybersecurity for Smart Devices
Despite the recent attacks on supermarkets, there is currently no evidence suggesting that domestic appliances are being specifically targeted. However, Ciaran Martin, the former CEO of the UK’s National Cyber Security Centre (NCSC), emphasizes the need for manufacturers to enhance the security of connected devices. He advises consumers to regularly update their devices and utilize multi-factor authentication to strengthen their defenses.
Since April 2024, UK legislation mandates that manufacturers of certain smart devices adhere to minimum cybersecurity standards, including secure password protocols and timely software updates. The NCSC is collaborating with global partners to assess the supermarket incidents but reports no known effects on the UK market.
Exposed Vulnerabilities in Retail Technology
Researchers from UK Cyber Defence have discovered over 800 refrigeration and building-control systems linked to British retailers that are accessible via the public internet. While this does not necessarily indicate they can be hacked, it does suggest that weak passwords and software flaws could leave them exposed to cyber threats.
The UK government has engaged in discussions with leading food retailers to bolster their cyber resilience following previous attacks. Helen Dickinson, CEO of the British Retail Consortium, has acknowledged that cyber incidents pose a significant threat, urging retailers to collaborate with the NCSC to enhance their cybersecurity measures. The past has shown that such hacks can disrupt food supplies, as seen when UK supermarkets faced challenges stocking shelves after ransomware attacks.
Tom Hegel, a researcher with SentinelOne, stresses the need for retailers to clarify their responsibility regarding the security of their equipment. He points out that while internet connectivity offers convenience, it also necessitates robust security measures. An attacker gaining control of essential functions could lead to severe disruptions, such as damaging perishable stock.
Broader Implications for Connected Technology
The potential vulnerabilities extend beyond supermarkets. Connected technology is increasingly used to manage industrial machinery and essential utilities. Cybersecurity expert Ken Munro recalls a 2015 incident where researchers hacked a Jeep through its internet-connected system, prompting significant improvements in automotive security.
While many UK utilities have secured their systems, Munro expresses concern about smaller, underfunded companies that may still rely on outdated technology. As Olivier Daloy from Zscaler points out, any internet-connected equipment, from manufacturers to infrastructure, could face similar cybersecurity risks.